THANK YOU FOR SUBSCRIBING
Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Healthcare Tech Outlook

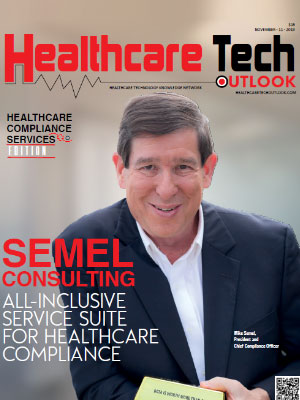
 Mike Semel, President & CCO, Semel Consulting
As Mike Semel, the President and Chief Compliance Officer of Semel Consulting, and the author of the best-selling ‘How to Avoid HIPAA Headaches’ points out, “Data is worth more than gold.” And, it is imperative for healthcare professionals to change their perspective toward data so that they will protect it in a better way, considering data privacy as well as compliance. Identifying this need, Nevada-based Semel Consulting assists healthcare providers and businesses that serve them in complying with the Health Insurance Portability and Accountability Act (HIPAA). “What makes us unique is that we help companies identify serious underlying issues, which they never knew existed in their organizations,” says Mike.
For instance, consider Semel Consulting’s recent engagement with a client. According to the client’s written policy, they were required to store all protected information on encrypted devices. Being unaware of the real picture, they believed that all their data was protected in encrypted devices. However, over the course of its engagement with the client, Semel Consulting identified data stored in vulnerable locations and that many of their devices were unencrypted. The firm helped the client resolve those issues, enabling them to prevent potential data breaches and the associated regulatory fines/ penalties.
Diagnosing and Fixing Issues at the Root
According to Mike, organizations spend too much time working on policies so that they fail to notice the issues that are making their networks and business components vulnerable to risks. While there are several compliance service providers that work toward helping these organizations, most of them adopt a questionnaire model—where healthcare organizations are asked to provide answers about their business components—for conducting risk analysis. Identifying that such methods won’t serve the need of today’s HIPAA compliance requirements, Semel Consulting adopts a “risk-first,” “doctor-like,” approach to prevent data breaches.
"It is imperative for healthcare professionals to change their perspective toward data so that they will protect it in a better way, considering data privacy as well as compliance"
“A doctor never treats patients by the information they provide. She usually instructs them to either take a blood test or X-Ray or MRI to identify the real problems. By looking at the test results and bringing that data into consideration, the doctor reaches her conclusion,” adds Mike.
As a cybersecurity and compliance consultant, Semel Consulting asks organizations about their issues, to get an outline of their problems. The company then runs separate tests to get to the core of the clients’ networks. The firm conducts a thorough check on the client’s devices to identify how their users are set up, the privileges, log in methods, and more. For example, in a recent engagement, Semel Consulting found that a few computers in the client’s network had no antivirus software and many systems were missing critical security patches and updates that they thought they were done with.

We offer training to help executives understand the significance of compliance and improve their proficiency with all their requirements

Such a result-driven approach helps Semel Consulting to provide pieces of evidence to organizations about potential issues in their networks, enabling them to fix those problems to secure data. This allows clients to pass the audit and avoid penalties or lawsuits that accompany a data breach.
The “Semel” Touch in Healthcare Compliance
The primary objective of Semel Consulting is to assist clients in complying with laws, industry requirements, contractual obligations, and insurance policy requirements. The firm works with HIPAA Privacy Rule—that safeguards patients’ protected health information (PHI)—to ensure that healthcare providers comply with the privacy practices and other requirements. It also assists organizations in aligning with the HIPAA Security Rule, which specifies the measures a company should implement to protect the confidentiality, integrity, and availability of patients’ electronic protected health information (ePHI). Semel Consulting also works with the HIPAA Breach Notification Rule, which requires the companies to notify affected individuals and government agencies about a data breach.
Semel Consulting is unique in its dual focus on state compliance laws as well as the federal requirements of HIPAA. “Complying with HIPAA doesn’t mean that an organization is in compliance with the state laws,” says Mike. For example, federal laws require organizations to notify patients about a data breach in 60 days. However, the firm has worked with clients in Texas and Florida, where patients have to be notified in 30 days as per the state laws. Entities in California are required to notify in 15 days. Semel consulting has a clear understanding of all these laws. Further, identifying that organizations have signed contracts with their partners who have multiple cybersecurity requirements, the firm has extended its footprint to contractual obligations as well. “We also work on cyber liability insurance where we assess our clients’ compliance against their own insurance policy,” adds Mike.
The Mark of a New Dawn
Since its inception, Semel Consulting’s primary focus was on delivering individual services to its clients. However, identifying the ever-increasing healthcare compliance requirements and recurrence of similar issues within space, the firm shifted to a “one-year consulting agreement” business model. This allows clients to glean the company’s comprehensive suite of services, including risk analysis and compliance assessments to identify the gaps that have to be remediated, throughout a year with no additional cost.
For example, in January 2017, Semel Consulting engaged with a company that delivered data analytics as a service. The client had to comply with HIPAA, the Florida Information Protection Act (FIPA) state law—and cybersecurity requirements of a large medical clinic, who was their client.
Semel Consulting conducted risk analysis and compliance assessments according to the client’s needs and sent them reports in January. Semel Consulting identified that the passwords once set in the client’s systems never expired—a major security issue, which the client’s IT department said was fixed in February. Later on, in June, Semel Consulting carried out a network scan for the client prior to the federal government’s HIPAA audit and detected the same issue. The client’s IT team resolved it on a priority basis. This was followed by another scan by the firm to make sure that the issue was rectified and ultimately allowed the client to pass the audit without any regulatory penalties or lawsuits. “We spent about 25 hours and never charged them a cent beyond what they had paid as the annual consulting fee,” says Mike. In another instance, Semel Consulting’s team spent more than 30 hours with a home healthcare organization that had private equity investors who wanted to validate the client’s HIPAA compliance to invest money. “Instances like this prove that compliance—which was once a checklist requirement of the government—has evolved into a component that can improve an organization’s overall value,” says Mike.
Semel Consulting also offers HIPAA training to help healthcare professionals understand the significance of HIPAA and improve their proficiency in HIPAA requirements. As a part of every project, the company trains clients’ top executives and senior-level managers. Dubbed as “executive briefing,” Semel Consulting will explain HIPAA in terms of data breaches, penalties, lawsuits, and other consequences from a business standpoint. Mike has also written two HIPAA training courses for 4Med Approved, a HIPAA training provider. The first is for compliance officers titled “Certified HIPAA Security Professional (CHSP)” and the second one is on “Certificate of HIPAA Workforce Proficiency (CHWP).”
Materializing a Compliant Future
Semel Consulting traces its roots to an IT company that delivered backup solutions to vindicate its goal of data security. Learning about HIPAA in 2003 and identifying that the federal government was going to require all healthcare organizations to comply with cybersecurity regulations, Mike transformed his company as a HIPAA specialist. With his long-standing experience—including his stint as the CIO of a hospital, handling its compliance requirements—Mike eventually drove Semel Consulting to success, by fulfilling the escalating needs of compliance in healthcare organizations and related businesses. Since its inception, the firm has also expanded its focus into identifying newer threats that affect healthcare organizations and help them align well with the changing regulatory requirements.
In the months to come, Semel Consulting has plans to recruit more certified healthcare compliance specialists who can deliver high-quality services, and in turn, help the company strengthen its position as a consulting firm. Semel Consulting is also planning to work with IT companies and departments to help them understand HIPAA and similar compliance requirements, including NIST Cybersecurity Framework (NIST CSF). To effectuate this, Semel Consulting is building self-paced online training courses and educating organizations around their compliance needs.
November 07, 2019

Company
Semel Consulting
Management
Mike Semel, President & CCO, Semel Consulting
Description
Semel Consulting specializes in certified HIPAA (and other) regulatory compliance, IT Security policies and procedures, and certified Business Continuity planning. The business has real-world experience managing compliance for hospitals, school districts, and other businesses. Semel has also created business continuity plans for organizations of all sizes that have been used for businesses to survive the Joplin tornado, Hurricane Irene, SuperStorm Sandy, and many smaller emergencies. HIPAA SOS (Security Officer Services), Business Continuity Planning, IT Security Policies & Procedures, and Compliance management are some of the solutions that the business offers